Using a VPN on Linux
Install the protected Debian or Ubuntu package, sign in, and press connect. The GTK interface remains unprivileged.
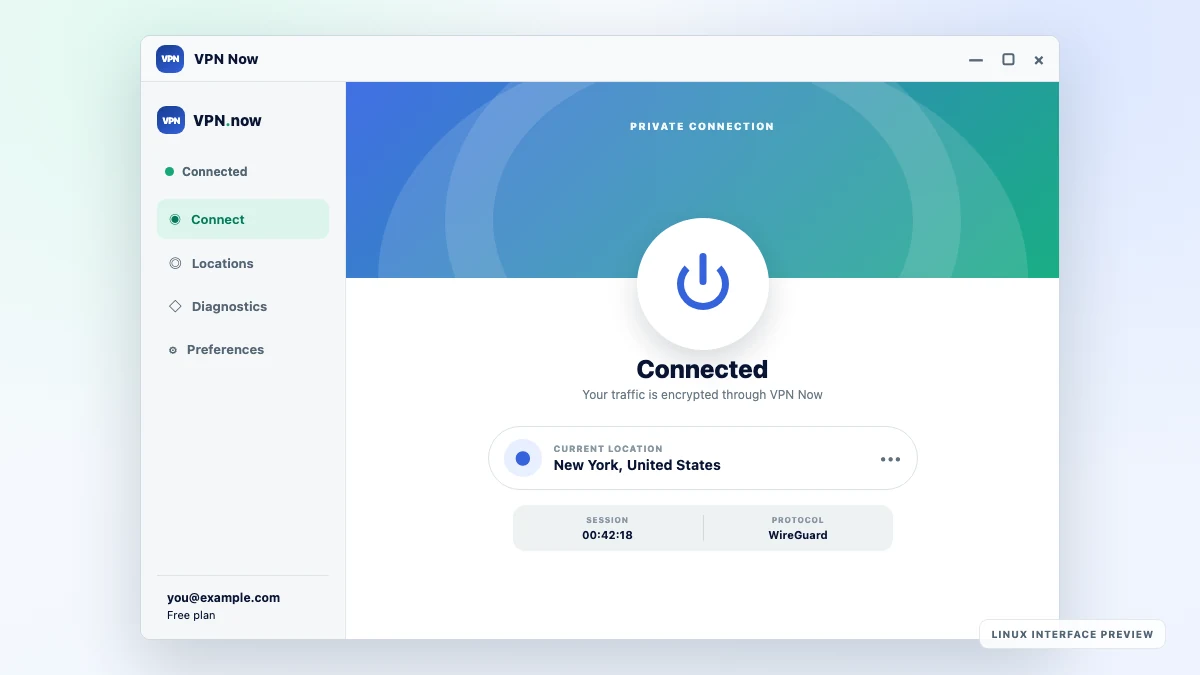
Get the vpn.now app for Linux
The fastest way to get started is our app: install it, sign in, and press connect. The manual steps below are here if you would rather set things up by hand.
Set up vpn.now on Linux
The whole process takes about five minutes. You will need a free vpn.now account before you start.
Step 1: Create your free account
Sign up for vpn.now with just an email address. No card needed, and the free plan does not expire.
Step 2: Download the vpn.now package
Get the .deb from the download page. It includes the app and installs the narrowly scoped tunnel helper with safe system ownership.
Step 3: Install and open it
Install the .deb with your software center or apt, then open vpn.now from the applications menu.
Step 4: Sign in and connect
Sign in with your email, or paste the activation code from your account, then press connect. Linux asks for authorization once to bring the connection up.
Prefer to configure things by hand? See the manual setup guide.
A modern VPN protocol, built into Linux
vpn.now runs on a modern VPN protocol that has been part of the mainline Linux kernel since version 5.6, back in 2020. It runs in kernel space, the same place your network stack lives, which keeps latency low and throughput high.
That is part of why Linux is such a good VPN platform. The vpn.now app sits on top and handles the rest: you sign in, press connect, and it does the work. If you want a refresher on what happens to a packet inside the tunnel, see how VPNs work.
One app, no terminal required
The vpn.now package gives you a simple window: pick a location and press connect. The interface runs as your user; only the fixed tunnel helper is privileged.
Prefer a panel toggle? GNOME and KDE can manage the connection through their own network settings once it is running. Either way, the app keeps the details out of your way.
Servers, containers, and the rest of your network
You can also push the VPN below your devices entirely. Running it on a router or a small Linux box protects every device behind it, including ones that cannot run a VPN themselves. Our guide to running a VPN on a router covers the tradeoffs and the setup.
What you need
- A 64-bit Linux desktop with GTK 4
- A free vpn.now account
- polkit and WireGuard tools (installed automatically by apt)
Having trouble? Our setup help section covers the most common issues, or you can contact support.
Linux VPN questions
Which Linux distributions are supported?
The complete package currently supports modern 64-bit Debian and Ubuntu desktops. Other distributions can use manual setup until signed RPM or native packages are available.
Do I need to use the terminal?
No. The vpn.now app has a simple window: sign in, pick a location, and press connect. GNOME and KDE can also manage the connection from their own network settings once it is running.
Does vpn.now support older VPN protocols on Linux?
No. vpn.now runs on one modern VPN protocol only, and the app handles it for you. There is nothing extra to configure and no certificates to manage.
Can I run vpn.now on a headless server?
Yes, though the app is built for the desktop. For headless machines, contact support and we will help you get connected without locking yourself out over SSH.
Using other devices too?
One vpn.now account covers all your devices. Set up the rest in minutes.
Protect your Linux device today
Set up takes minutes. vpn.now is free, with unlimited data and no card needed.
Get started free